A massive security flaw called “PHP2Shell” (CVE-2026-109618 / 109619) was just discovered. It affects the core software powering your server, allowing hackers to take over websites completely.
Updating your WordPress plugins, themes, or core WILL NOT FIX THIS. Only your hosting provider can patch it.
🛑 What You Need to Do Right Now:
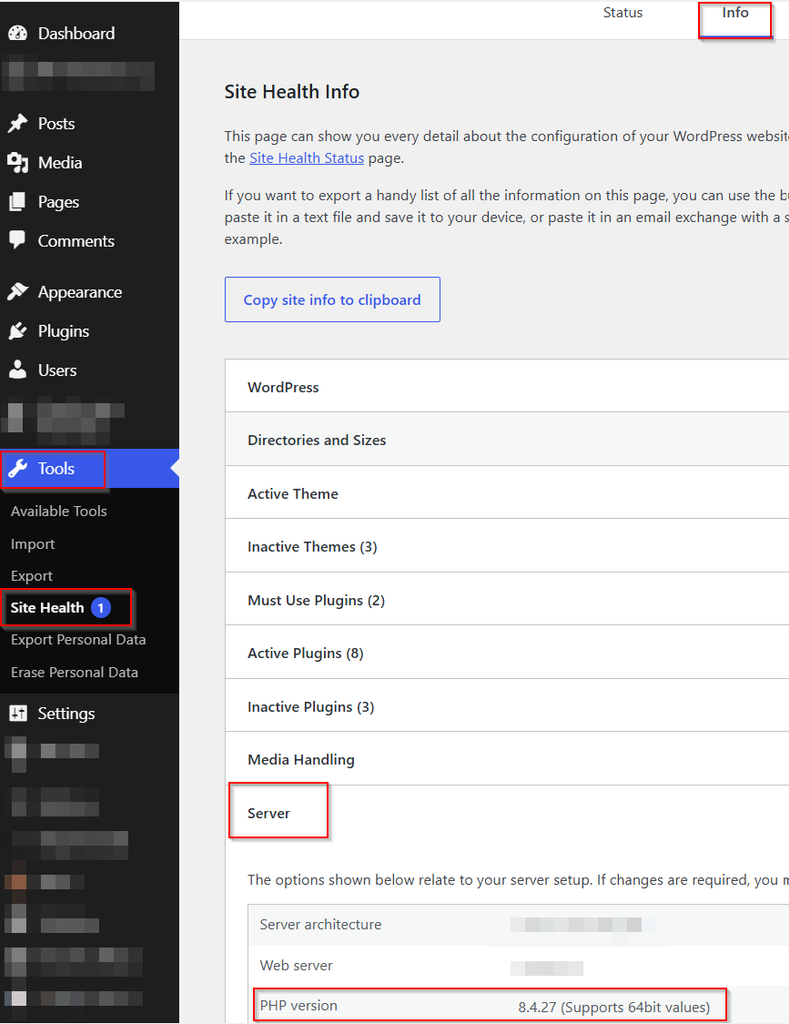
- Check your PHP Version: Log into WordPress, go to Tools > Site Health > Info > Server, and find your PHP version.
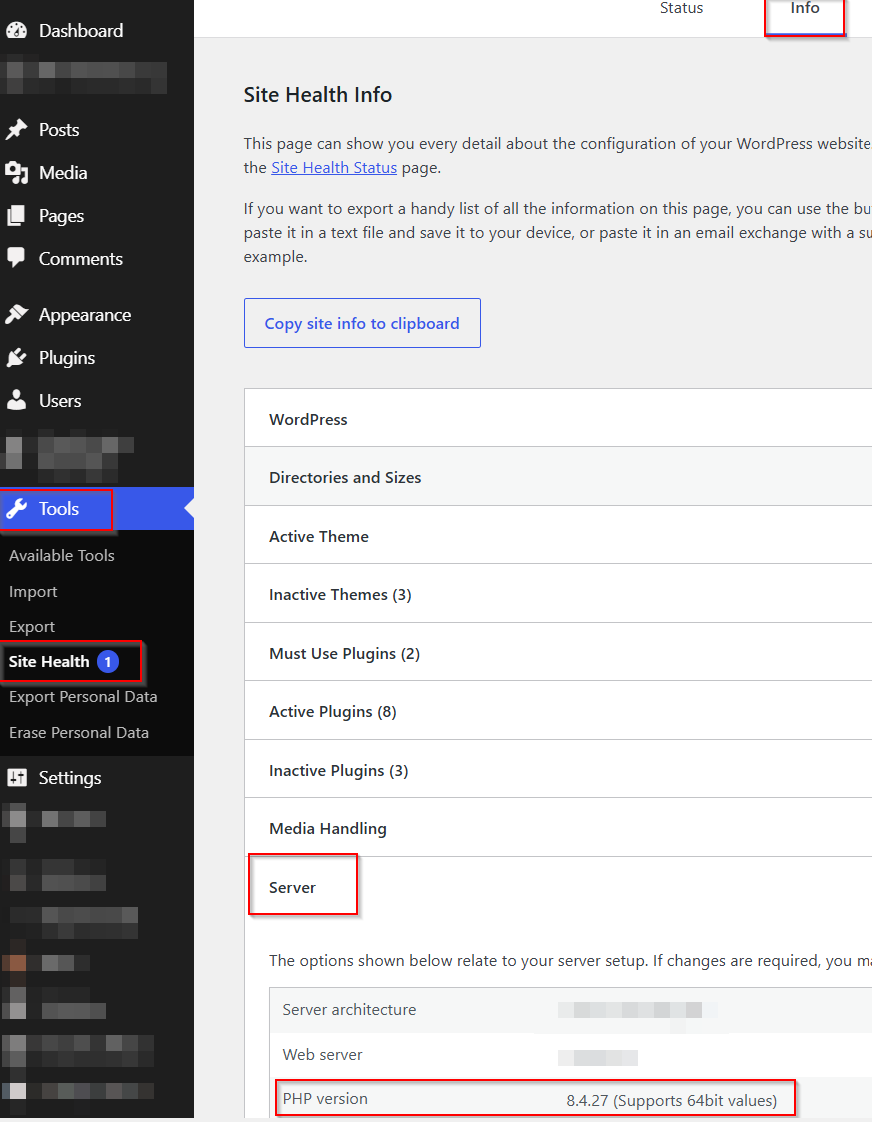
- Verify your patch level: You are safe only if your server runs:
- 8.5.12 or higher
- 8.4.27 or higher
- 8.3.36 or higher
- 8.2.35 or higher
- Contact your host: If your version is lower than these, open a live chat or support ticket with your web host ( For Example: Bluehost、Hostinger、SiteGround、WP Engine immediately and ask them to upgrade your PHP version to the latest secure patch.
- Where immediate remediation is not feasible, organisations/site owners should consider taking the system offline until it can be fully mitigated.
Don’t wait—security firewalls cannot fully block this exploit. Pass this on to anyone you know who manages a WordPress site!